RBAC
Roles and bindings. The diagram that finds the over-permissive service account.
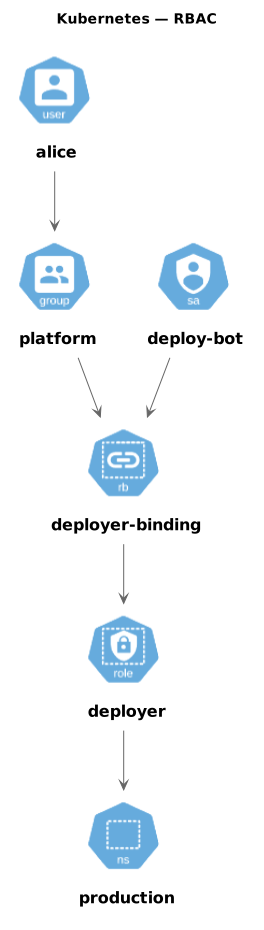
- Format.puml
- Length26 lines
- LibraryKubernetes icons
The source
26 lines of PlantUML, and pulls in Kubernetes icons. Copy it, or open the template inside Gnomon and render it as it is.
@startuml
!define KubernetesPuml https://raw.githubusercontent.com/dcasati/kubernetes-PlantUML/master/dist
!include KubernetesPuml/kubernetes_Common.puml
!include KubernetesPuml/kubernetes_Simplified.puml
!include KubernetesPuml/OSS/KubernetesUser.puml
!include KubernetesPuml/OSS/KubernetesGroup.puml
!include KubernetesPuml/OSS/KubernetesSa.puml
!include KubernetesPuml/OSS/KubernetesRole.puml
!include KubernetesPuml/OSS/KubernetesRb.puml
!include KubernetesPuml/OSS/KubernetesNs.puml

title Kubernetes — RBAC

KubernetesUser(user, "alice", "human")
KubernetesGroup(group, "platform", "")
KubernetesSa(sa, "deploy-bot", "in-cluster")
KubernetesRole(role, "deployer", "namespaced")
KubernetesRb(rb, "deployer-binding", "")
KubernetesNs(ns, "production", "")

user --> group
group --> rb
sa --> rb
rb --> role
role --> ns
@enduml
Render this offline
This template ships in Gnomon and renders on your machine, with no account and nothing sent to a server. The browser editor is free and needs no install.
Others in Kubernetes diagrams
- Cluster OverviewThe whole cluster at a glance. The one to draw first.
- Ingress to PodsIngress to service to pods. How traffic actually gets in.
- Workload and ConfigurationDeployments with their config and secrets attached.
- Stateful StoragePersistent volumes and claims. What survives a restart, and what does not.